As I read https://community.infoblox.com/t5/IPv6-CoE-Blog/Where-Are-You-On-The-IPv6-Adoption-Curve/ba-p/11116, I couldn't help but think of the progression of IPV6 support in UEFI.
We compared the adoption arc of the two efforts in
http://www.uefi.org/sites/default/files/resources/A_Tale_of_Two_Standards_0.pdf.
Interesting milestones on both the technology front https://tools.ietf.org/rfc/rfc5970.txt and in the specification uefi.org / codebase tianocore.org curation are shown below

Lots of changes these last few years. Another journey on this trip was meeting Paul Otellini in 2005. I was definitely saddened by the news https://www.theverge.com/2017/10/3/16411480/paul-otellini-death-intel-ceo
 But change is part of the trip. I recently said good bye to my colleague Lee Leahy. He and I collaborated for several years and had the opportunity to co-present https://www.youtube.com/watch?v=I08NHJLu6Us

To remind us that he has retired to Hawaii, he left the following picture in the cubicle behind mine, taken from his new backyard.

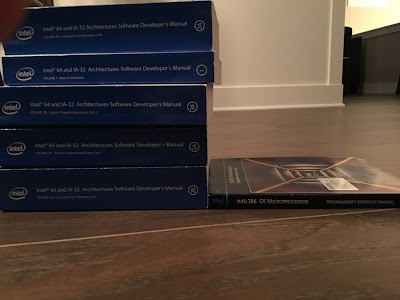
A final marker of the change occurred when cleaning out some data books. The right hand side (RHS) is the programmers reference manual (PRM) for the 386SX, whereas the left hand side (LHS) stack includes the reference tomes for an Intel based CPU's from a couple of years ago (prior to all documents going online-only).
 An example of the change include the RHS PRM description of an instruction such as SCAS. The description even listed the number of clocks to retire the instruction, which was possible in the days of simpler memory hierarchies, in order execution, etc.
 The following shows the same instruction from the LHS.

More modes. No clocks. As times change, instructions change.
I look forward to chatting with people on Sunday about UEFI and security https://firmwaresecurity.com/2017/10/10/uefi-security-presentation-at-seattle-dc206-meeting/. It's interesting to see this talk having been referenced in a few places, such as https://www.cylance.com/en_us/blog/black-hat-vegas-where-the-guardians-of-the-bios-are-failing.html, https://medium.com/@matrosov/bypass-intel-boot-guard-cc05edfca3a9, https://www.darkreading.com/vulnerabilities---threats/7-hardware-and-firmware-hacks-highlighted-at-black-hat-2017/d/d-id/1329442?piddl_msgorder=&image_number=6, and https://cloudplatform.googleblog.com/2017/08/Titan-in-depth-security-in-plaintext.html, too.
Speaking of change, time to break away from the PC.
PS
Update from 10/18/2017
Thanks to the Lodge

for great questions and attendance this weekend

We compared the adoption arc of the two efforts in
http://www.uefi.org/sites/default/files/resources/A_Tale_of_Two_Standards_0.pdf.

In 2010 my colleague Bob Hale and I noted the following about Tiano www.tianocore.org
 https://github.com/vincentjzimmer/Documents/blob/master/Neither-Seen-Nor-Heard.pdf. 9th generation in 2009. Oh my. Good thing we chose a different designation for the various types we snap EDKII trunk with the validated UDK releases https://github.com/tianocore/tianocore.github.io/wiki/UDK


To remind us that he has retired to Hawaii, he left the following picture in the cubicle behind mine, taken from his new backyard.

A final marker of the change occurred when cleaning out some data books. The right hand side (RHS) is the programmers reference manual (PRM) for the 386SX, whereas the left hand side (LHS) stack includes the reference tomes for an Intel based CPU's from a couple of years ago (prior to all documents going online-only).


I look forward to chatting with people on Sunday about UEFI and security https://firmwaresecurity.com/2017/10/10/uefi-security-presentation-at-seattle-dc206-meeting/. It's interesting to see this talk having been referenced in a few places, such as https://www.cylance.com/en_us/blog/black-hat-vegas-where-the-guardians-of-the-bios-are-failing.html, https://medium.com/@matrosov/bypass-intel-boot-guard-cc05edfca3a9, https://www.darkreading.com/vulnerabilities---threats/7-hardware-and-firmware-hacks-highlighted-at-black-hat-2017/d/d-id/1329442?piddl_msgorder=&image_number=6, and https://cloudplatform.googleblog.com/2017/08/Titan-in-depth-security-in-plaintext.html, too.
Speaking of change, time to break away from the PC.
PS
Update from 10/18/2017
Thanks to the Lodge

for great questions and attendance this weekend


